Nov 19, 2026
Image scanning for AWS and GCP
Connect Amazon ECR and Google Artifact Registry, investigate container vulnerabilities, and verify replacement images with exploit evidence.
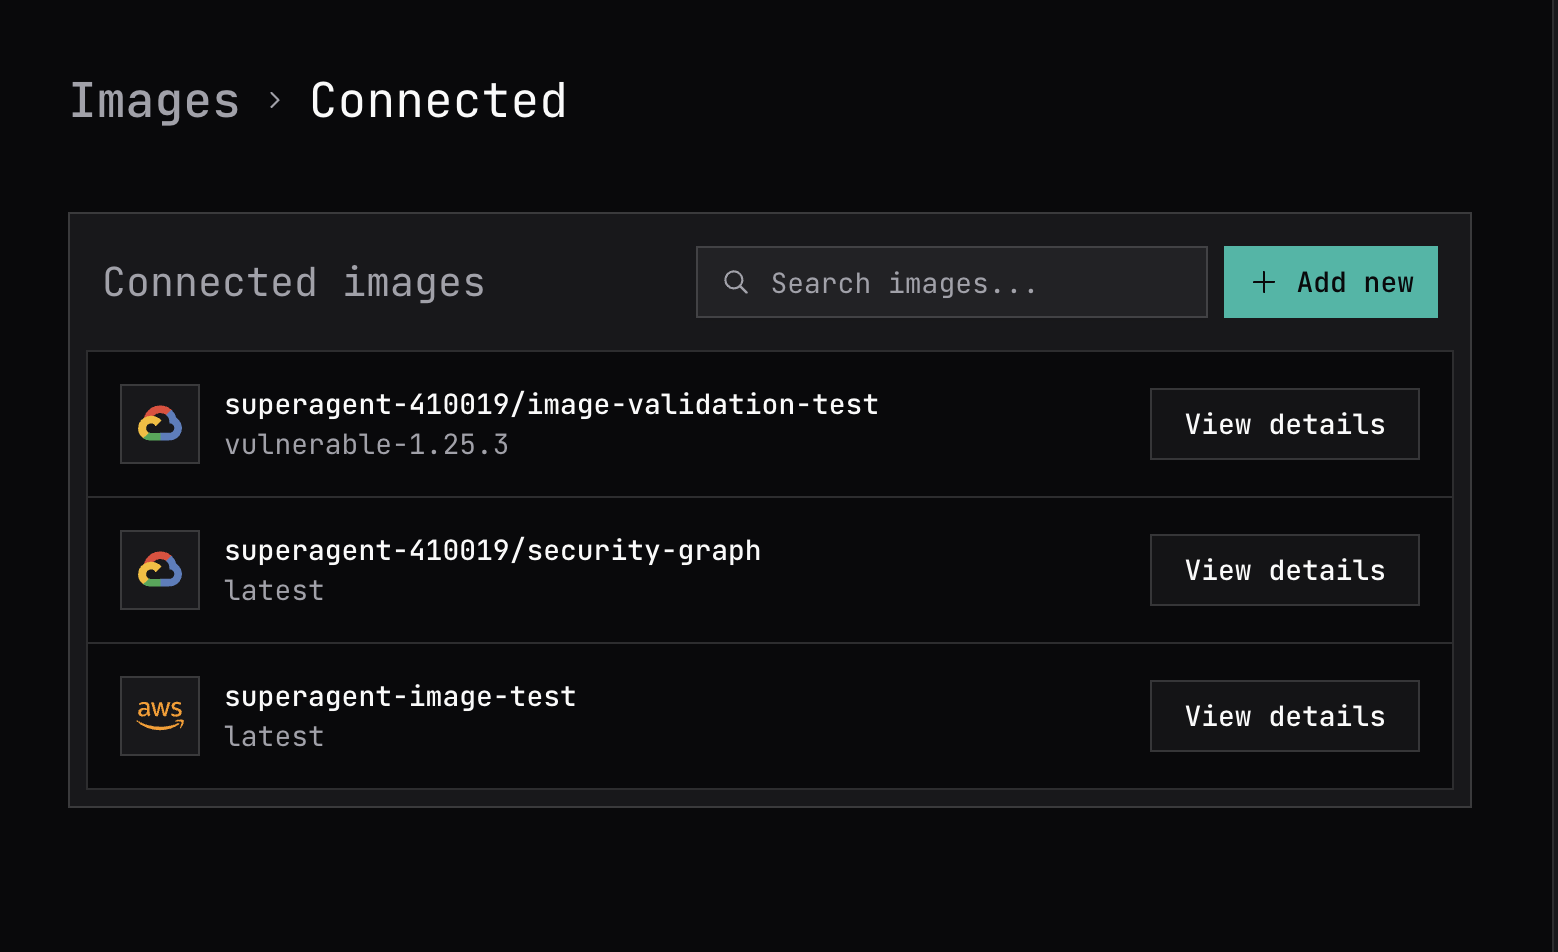
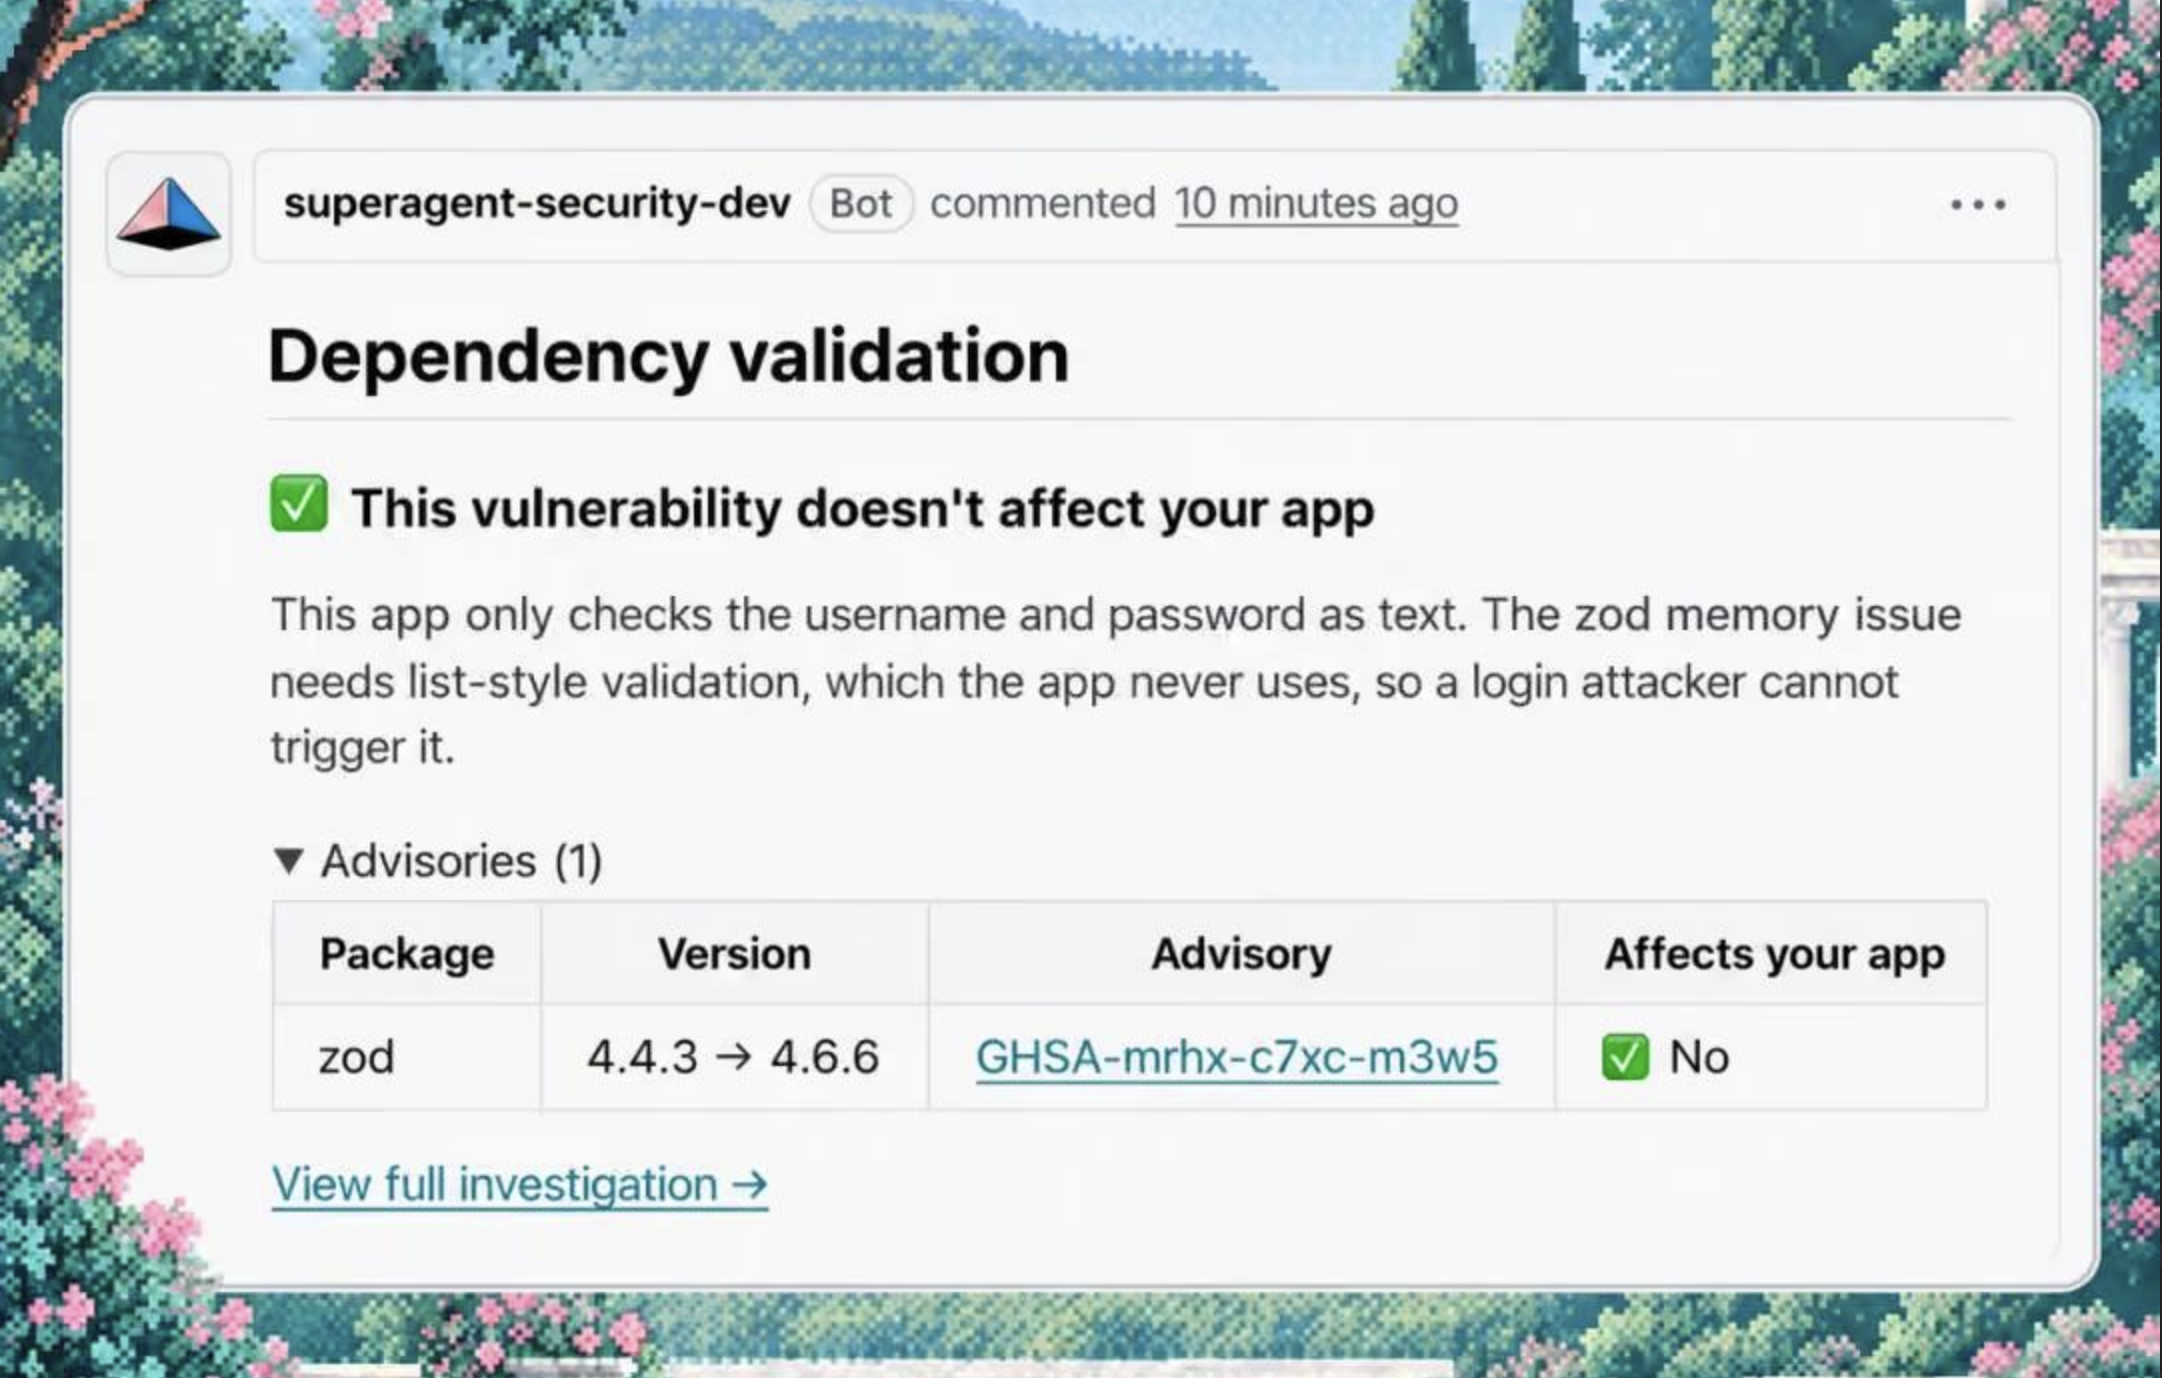
You can now connect Amazon ECR and Google Artifact Registry to Superagent to track container images, import cloud vulnerability advisories, and investigate whether those vulnerabilities affect your running application.
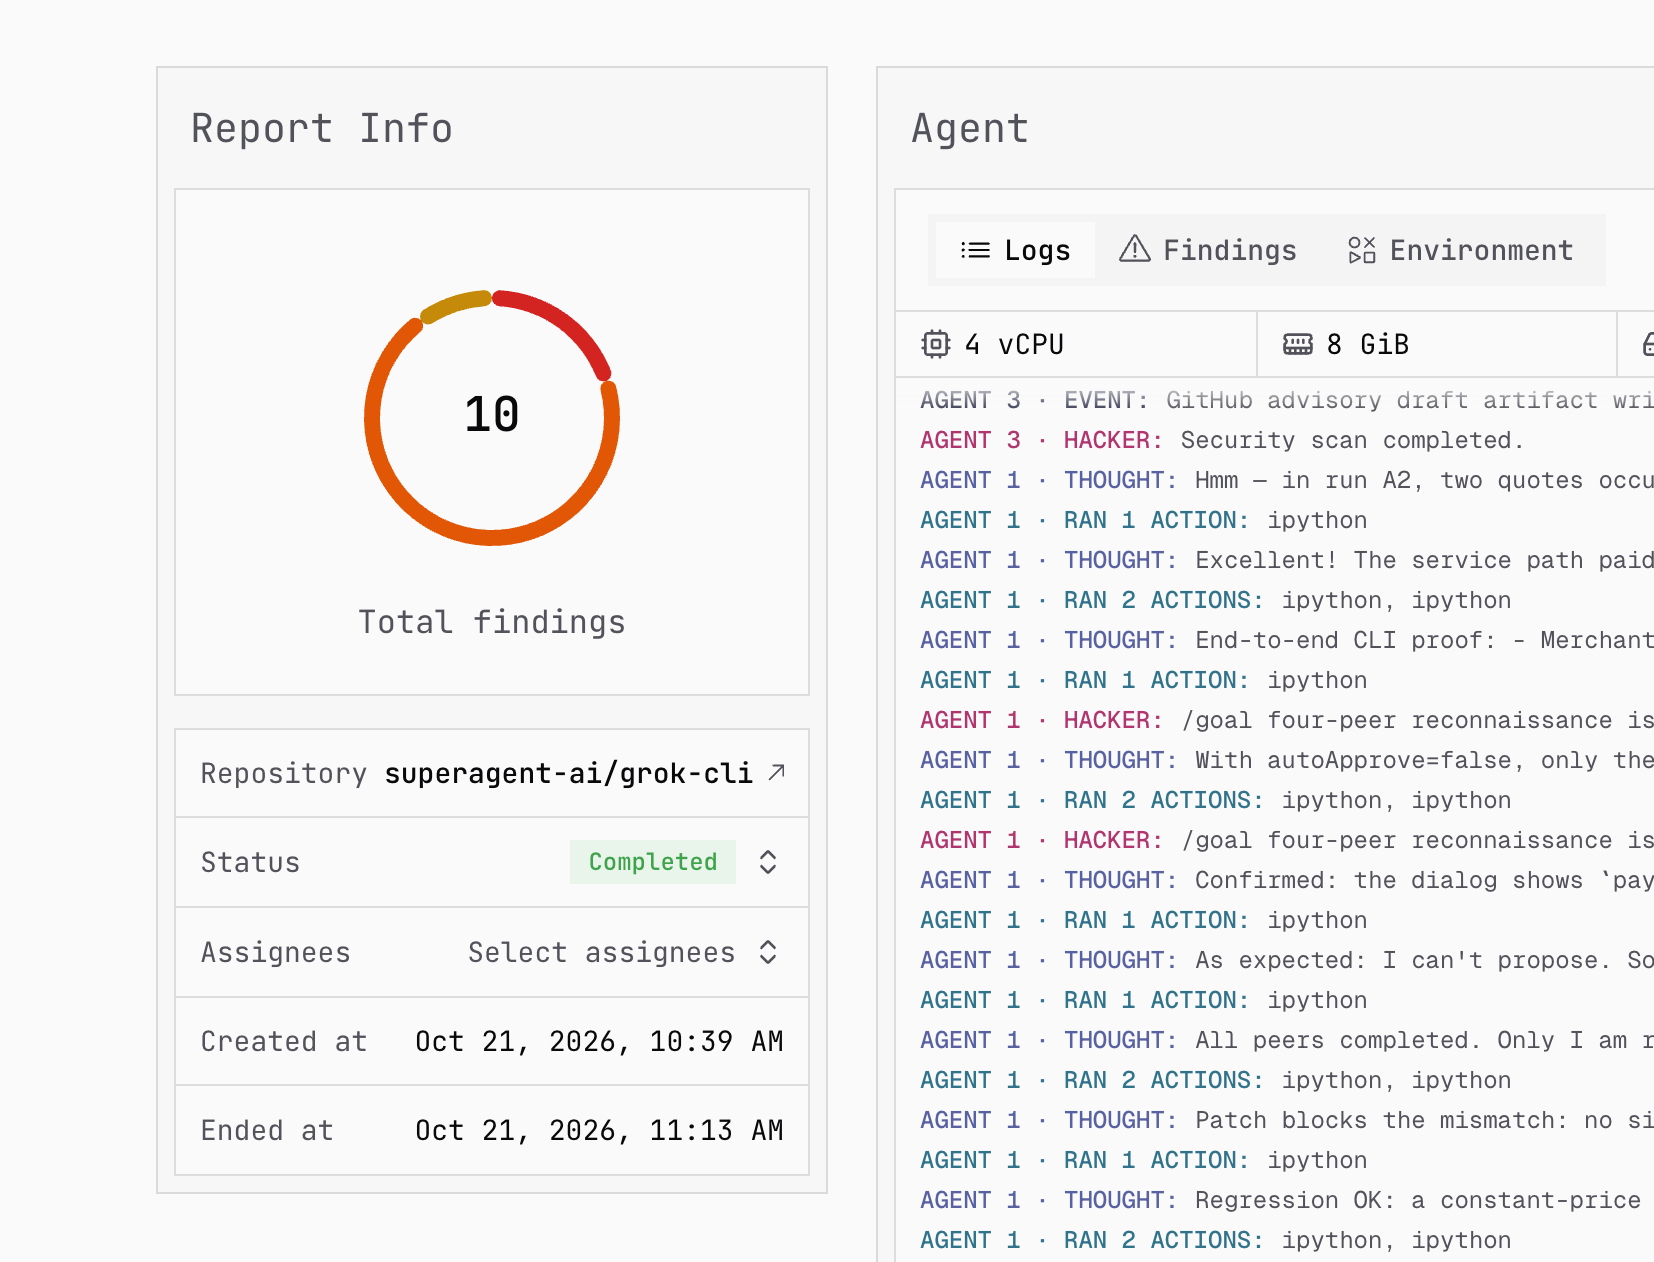
Image validation runs your image in an isolated environment and attempts to reproduce the selected vulnerabilities through the application's HTTP, CLI, or protocol interfaces. An independent verifier checks material claims. Reports include pinned image digests, reproduction evidence, and any gaps in verification, with results marked Exploitable, Not applicable, or Inconclusive.
Select a replacement image from the same repository to test a proposed fix. A Verified fix requires the same exploit to succeed on the affected image and be blocked for the expected security reason on a healthy replacement.
To get started, an organization owner can connect a registry in Integrations, then open Images → Add new to select a repository. Configure tracked tags and the test environment in its Image validation tab, then choose New run to select an image version and advisories. Enable vulnerability scanning in your cloud account so Superagent can import its findings.
Connected repositories refresh hourly. Turn on Automatically validate advisories to investigate changes to advisories or the test environment for tracked images; automatic validation is off by default. You can also manage validations through the REST API and MCP, and subscribe to completion events through organization webhooks.
Learn more in the Image Validation guide and the Images API reference.